NEW QUESTION 64
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure application gateway that has Azure Web Application Firewall (WAF) enabled.
You configure the application gateway to direct traffic to the URL of the application gateway.
You attempt to access the URL and receive an HTTP 403 error. You view the diagnostics log and discover the following error.
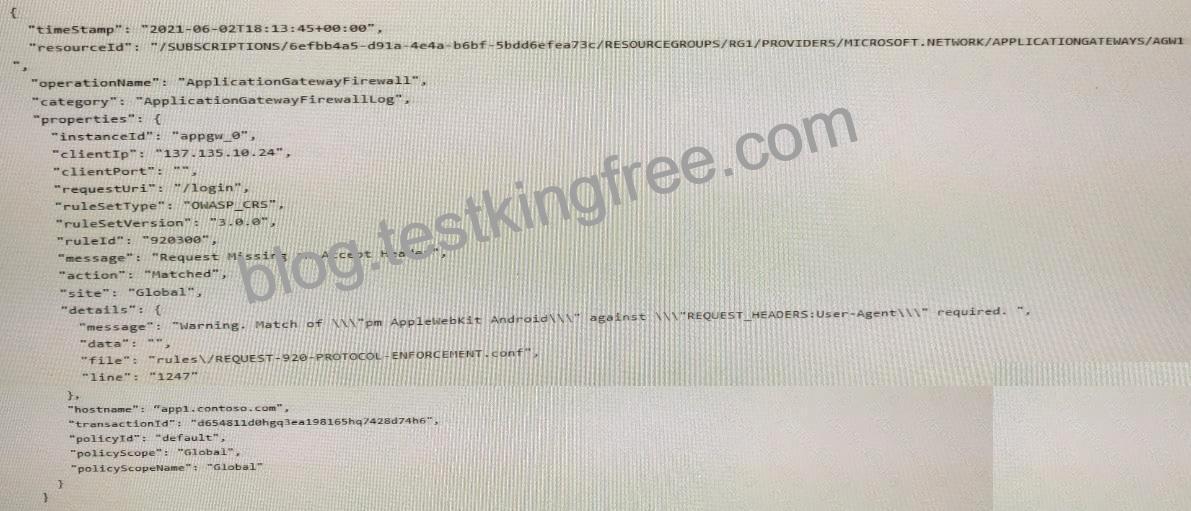
You need to ensure that the URL is accessible through the application gateway.
Solution: You configure a custom cookie and an exclusion rule.
Does this meet the goal?
Topic 2, Litware. Inc Case Study 1
Overview
Litware. Inc. is a financial company that has a main datacenter in Boston and 20 branch offices across the United States. Users have Android, iOS, and Windows 10 devices.
Existing Environment:
Hybrid Environment
The on-prernises network contains an Active Directory forest named litwareinc.com that syncs to an Azure Active Directory (Azure AD) tenant named litwareinc.com by usinq Azure AD Connect.
All the offices connect to a virtual network named Vnetl by using a Site-to-Site VPN connection.
Azure Environment
Litware has an Azure subscription named Sub1 that is linked to the litwareinc.com Azure AD tenant. Sub1 contains resources in the East US Azure region as shown in the following table.
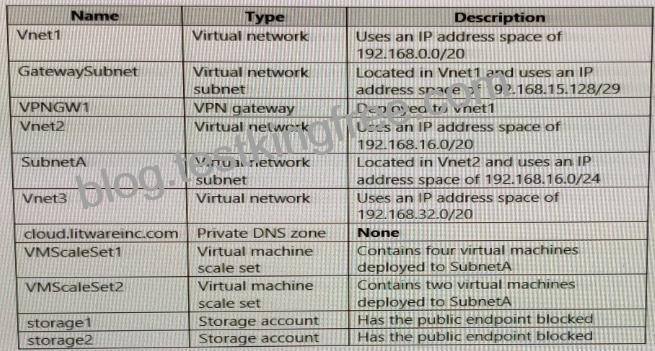
There is bidirectional peering between Vnet1 and Vnet2. There is bidirectional peering between Vnet1 and Vnet3. Currently, Vnet2 and Vnet3 cannot communicate directly.
Requirements:
Business Requirements
Litware wants to minimize costs whenever possible, as long as all other requirements are met.
Virtual Networking Requirements
Litware identifies the following virtual networking requirements:
* Direct the default route of 0.0.0.0/0 on Vnet2 and Vnet3 to the Boston datacenter over an ExpressRoute circuit.
* Ensure that the records in the cloud.litwareinc.com zone can be resolved from the on-premises locations.
* Automatically register the DNS names of Azure virtual machines to the cloud.litwareinc.com zone.
* Minimize the size of the subnets allocated to platform-managed services.
* Allow traffic from VMScaleSet1 to VMScaleSet2 on the TCP port 443 only.
Hybrid Networking Requirements
Litware identifies the following hybrid networking requirements:
* Users must be able to connect to Vnet1 by using a Point-to-Site (P2S) VPN when working remotely.
Connections must be authenticated by Azure AD.
* Latency of the traffic between the Boston datacenter and all the virtual networks must be minimized.
* The Boston datacenter must connect to the Azure virtual networks by using an ExpressRoute FastPath connection.
* Traffic between Vnet2 and Vnet3 must be routed through Vnet1.
PaaS Networking Requirements
Litware identifies the following networking requirements for platform as a service (PaaS):
* The storage1 account must be accessible from all on-premises locations without exposing the public endpoint of storage1.
* The storage2 account must be accessible from Vnet2 and Vnet3 without exposing the public endpoint of storage2.